Published facts about a real business incident.
CASE STUDIES / REAL INCIDENTS & LAB RESULTS
Real incidents.
Evidence from the Lab.
Explore a real incident, the scenario we reconstructed from it, and the report DutAIx returned.
Examine the case studyThe use cases we reconstructed from those facts, run through the Requirements module in DutAIx.
The duties and gaps DutAIx identified, and the points that still need human review.
REAL INCIDENT CASE STUDY
An automated credit decision that could not explain itself.
A financial-services provider in the EU used automated, algorithm-based decisions to assess credit-card applications. Several applicants with good creditworthiness were rejected. The decisions were made without human intervention. When applicants asked why, the provider did not give adequate information about the logic, significance or consequences, and did not meet its information and access obligations. The authority fined the company EUR 492,000.
What we have done: we reconstructed the credit-card decision and applicant-rights scenario as a normal project and executed it in the DutAIx Requirements module.
We do not claim the provider used AI. The published facts describe automated, algorithm-based decisions; we assume AI could have been in scope. This is not an assurance that the incident would have been prevented and is not legal advice.
WHAT THE LAB IDENTIFIED
Acts and gaps.
4stories assessed22applicable now13story-level duties9project-level duties
GDPR
- Article 5Purpose, minimisation, retentionPotential gap
- Article 6Lawful basisPotential gap
- Articles 13–14Information about automated decisionsPotential gap
- Articles 15 & 17Access, correction, erasurePotential gap
- Article 22Human review and contestPotential gap
- Article 25Data protection by designNot evidenced
- Article 30Record of processingNot evidenced
- Article 32Security of processingPotential gap
- Article 33Breach notificationNot evidenced
- Article 35DPIA before go-livePotential gap
EU AI Act
- Article 4AI literacyPotential gap
- Article 5Prohibited practices screeningNot evidenced
- Article 6, Annex III, Article 49Risk classification and registrationNot evidenced
- Article 12Automatic loggingNot evidenced
- Article 14Human oversight and automation biasPotential gap
- Article 50AI interaction transparencyPotential gap
Executed the Requirements module only for this case study. Design, Build and QA modules were not run.
THE REPORT RETURNED
The actual report.
Inside the report
- Gaps identified against each submitted story
- Suggested changes and acceptance details for review
- 13 story-level + 9 project-level duties, with acts
- Audit trail and evidence record
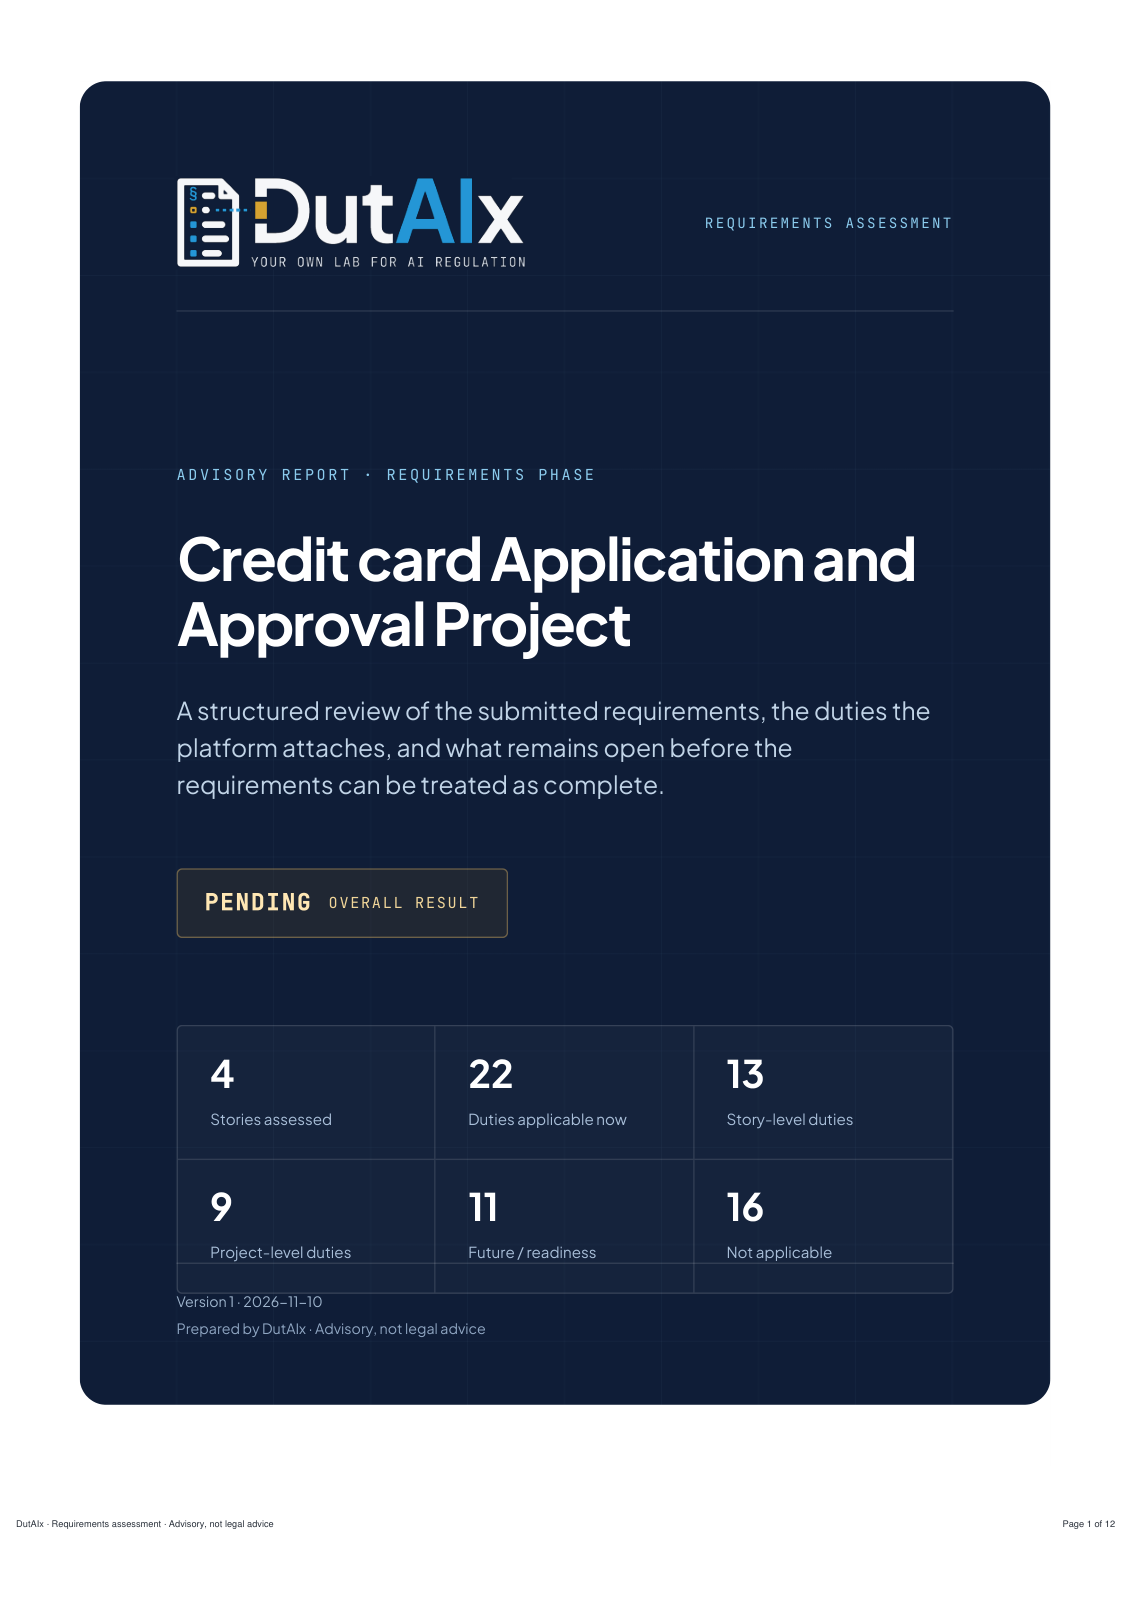 PDF · 12 PAGES
Requirements only · 4 stories · Version 1.
The PDF is advisory and not a legal opinion or compliance certificate.
SEE THE PLATFORM IN PRACTICE
Inspect the evidence.
Ask the next question.
See how the platform supports a practical review in a walkthrough.
Request a walkthrough